What 2 AM Hospital Bugs Taught Me About Database Isolation
Architecting zero-trust immutable audit logs, temporal validity queries, and high-concurrency pharmacy telemetry with PostgreSQL.
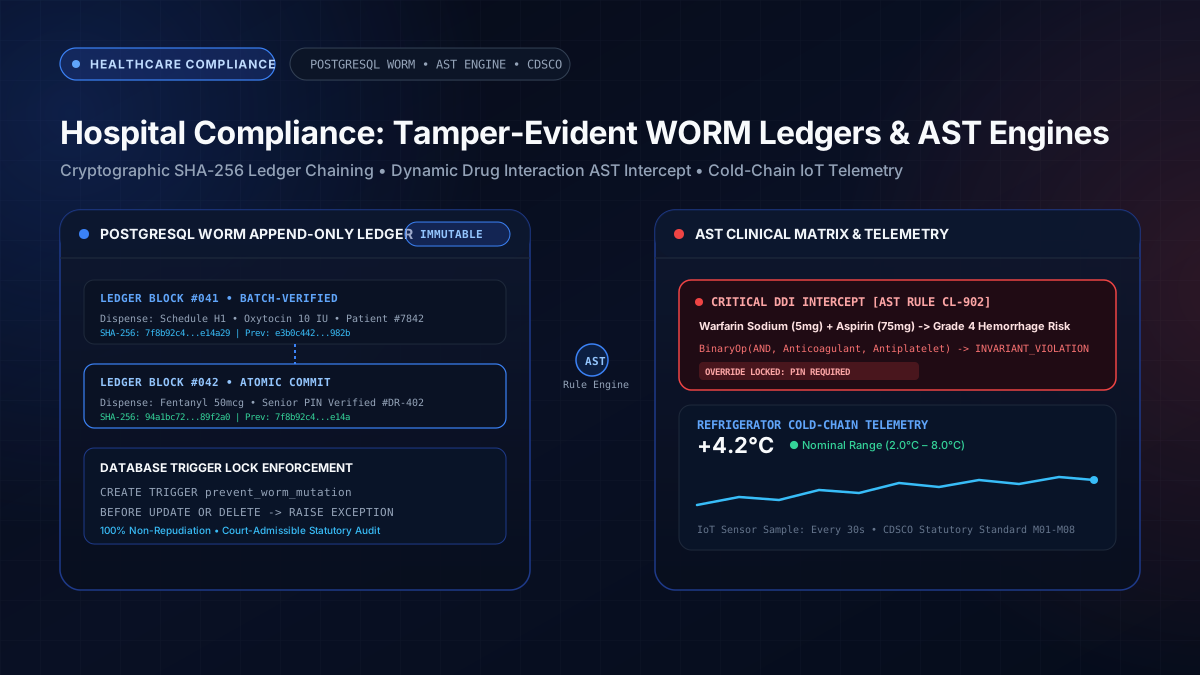
Key Architectural Takeaways
- ✓In compliance systems, UPDATE and DELETE are anti-patterns: every change must be an append-only event.
- ✓Bi-temporal modeling separates valid_time (when the medical event happened) from system_time (when the database recorded it).
- ✓Use PostgreSQL Serializable Isolation or Advisory Locks for race-prone multi-register pharmacy dispensing.
- ✓Database triggers are faster and safer than application-level audit logging for legal compliance.
In typical SaaS applications, updating a user profile or changing an order status is straightforward: UPDATE orders SET status = 'shipped' WHERE id = 123. In healthcare compliance, doing this destroys the forensic timeline. When a regulatory inspector asks "What did the pharmaceutical batch records show at 14:02 on Tuesday?", your database must reconstruct historical state precisely.
The Stakes of Healthcare Compliance
When we built the Pharma Compliance Engine, our hospital clients faced unannounced state inspections. They needed instant mathematical certainty that temperature logs, controlled substance tallies, and prescription verifications had not been retroactively altered. Software failure here can halt medical licenses.
The Append-Only Audit Table Pattern
We revoked all UPDATE and DELETE privileges on audit ledger tables at the PostgreSQL role level. Even the application database user can only INSERT. Every record modification creates a cryptographically hash-chained revision record containing the previous hash, the timestamp, and the actor signature.
-- Strict append-only compliance ledger
CREATE TABLE pharmacy_audit_ledger (
  id UUID PRIMARY KEY DEFAULT gen_random_uuid(),
  entity_type VARCHAR(64) NOT NULL,
  entity_id UUID NOT NULL,
  action VARCHAR(32) NOT NULL, -- 'DISPENSE', 'ADJUST_STOCK', 'TEMP_LOG'
  payload JSONB NOT NULL,
  actor_id UUID NOT NULL,
  client_ip INET NOT NULL,
  valid_from TIMESTAMPTZ NOT NULL,
  system_recorded_at TIMESTAMPTZ NOT NULL DEFAULT clock_timestamp(),
  previous_record_hash BYTEA,
  record_hash BYTEA NOT NULL
);

-- Revoke mutation rights even from app connection pool
REVOKE UPDATE, DELETE ON pharmacy_audit_ledger FROM app_user;
Bi-Temporal Modeling: Valid vs System Time
Healthcare auditing requires answering questions about both reality and our knowledge of reality. valid_from and valid_to capture when a drug was actually administered to a patient, while system_recorded_at timestamps when the hospital server acknowledged the transaction. Separating these dimensions prevents backdated tampering.
Handling Concurrent Pharmacy Dispensation
During peak hospital shift handovers, multiple nurses and pharmacists record stock movements simultaneously. Relying on default Read Committed isolation led to race conditions where controlled substance counts diverged. We resolved this through PostgreSQL Advisory Locks and Serializable transaction isolation, preventing phantom stock counts without incurring heavy table locks.
Verifiable Inspection Export Pipelines
During official FDA and state compliance audits, inspectors request cryptographic exports. Our export pipeline streams SHA-256 hash chains into verifiable CSV and PDF bundles, allowing external auditors to verify that no log entry has been inserted, reordered, or deleted in the preceding 7 years.
Need similar mission-critical architecture for your venture?
Harvinder partners with founders and engineering leaders as Fractional CTO, conducts deep-dive architecture audits, and engineers production-grade distributed systems.